New tools and some docs..

Hi i'm back from the vacations, i will start posting more frequently than before, it's an objetive that i set.

Well let's move on the first post, it is about some new tools and documents from the last weeks.

Docs:

Blackhat and Defcon are over, and the presentations and whitepapers could be downloaded from here:

Blackhat: http://164.106.251.250/docs/netsec/bh2007/
Defcon: http://164.106.251.250/docs/dc15/

There are a lot of presentations, and some are really good.


Tools:

Nmap-SOC:
First Nmap SOC release! Nmap 4.22SOC1

The new nmap version is available, with all the improvements proposed in the Summer Of Code (Google). Some of the highlights are:

-The UMIT graphical Nmap frontend is now included
-The port selection mechanism was overhauled
-Added the --reason option which explains WHY Nmap assigned a port status
-Integrated all of your 2nd generation OS detection submissions, increasing the database size by 68% since 4.21ALPHA4 to 699 fingerprints.
-Added --servicedb and --versiondb command-line options which allow you to specify a custom Nmap services (port to port number translation and port frequency) file or version detection database.
-In verbose mode, Nmap now reports where it obtains data files (such as nmap-services) from.

These are some of the more significant (at least for me), there are many more improvements on the release.

Information: http://seclists.org/nmap-dev/2007/q3/0030.html


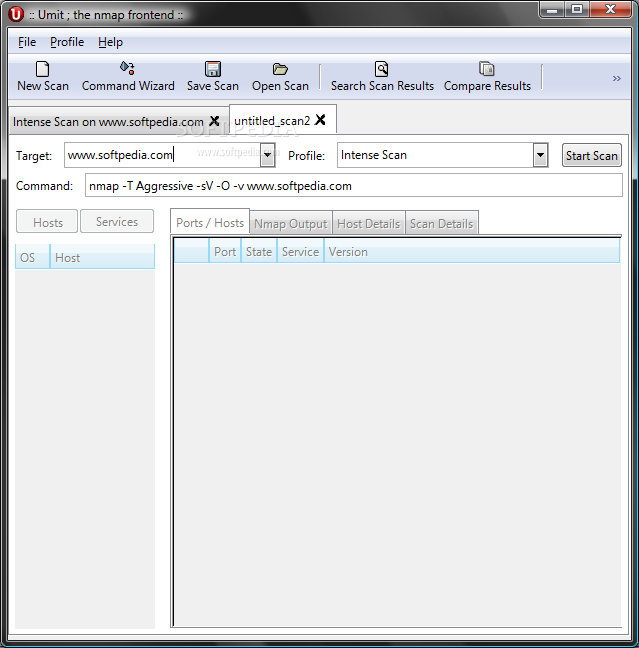
Umit: Nmap frontend.

Really a very good frontend, with a lot of functionalities, like comparing between different scans, saving scans, multiple tabs, profiles, information highlighting, etc. This project is sponsored by the Google Summer Of Code.

Install: http://umit.sourceforge.net/install.html
Blog: http://umitproject.blogspot.com/


Evolution: Massive information Gathering.

Evolution is a program that can be used to determine the relationships and real world links between different entities. Really it worths a try. I liked a lot the GUI, is still in beta stage, but is really awesome the interface.

Presentations: http://www.paterva.com/web/Evolution/Presentations/
Web: http://www.paterva.com/web/Evolution/


Immunity Debugger:

The new toy from Immunity guys, this is a new debugger oriented for vulnerability analysis, and security related task. It's programmed in python :), you can load python scripts to aid the analysis. Immunity says:

-A debugger with functionality designed specifically for the security industry
-Cuts exploit development time by 50%
-Simple, understandable interfaces
-Robust and powerful scripting language for automating intelligent debugging
-Lightweight and fast debugging to prevent corruption during complex analysis
-Connectivity to fuzzers and exploit development tools


Really a very good tool.

Information: http://www.immunitysec.com/products-immdbg.shtml
Announce: http://seclists.org/bugtraq/2007/Aug/0047.html

That's all for today :)

Metasploit GUI & Assistant

After a long waiting, a cool Metasploit GUI is available. In the development version of the metasploit is available the GUI with the new Metasploit::Assistant.

I think this is a great advance, and step by step the project is getting near the commercial options (Canvas, Core Impact). Right now Metasploit has 187 exploits, 106 payloads and many more

One great thing of this Framework is that runs on the Nokia 770/800, i hope for the GUI to run on the Nokia soon, it will be very easy to hack on the move, not typing in the mini X-term. Someone to port ruby-libglade and ruby-gtk2?


Next, Next, Next, Own3d ;)


For installing in Backtrack2 Final:

1-Download the following files:

ruby-gtk2
ruby-libglade2

2-Execute these commands:

# lzm2dir ruby-gtk2-0.16.0.lzm /
# lzm2dir ruby-libglade2-0.16.lzm /

# cd /pentest/exploits/framework3
# svn update
# ./msfgui


And here are some screenshots of the GUI running:


Wfuzz update!

We did some bug cleaning, and some improvements to our wfuzz. Now it supports colored output on Windows machines!, we added support for fuzzing all GET and POST variables with one command, and we also tackle some errors.

If you find an error please send us an email, also if you have a new dictionary please help with the project and send it to us ;)

Check the new version: Wfuzz

My new Nokia 770!

Im very happy with my new Nokia 770, its an Internet Tablet that is between a mobile phone and a mini computer. It has an ARM processor, MMC memory, Wlan, Bluetooth, and an impressive 800x480 screen.

The cool thing is that is based on Debian Linux (Kernel 2.6.12). I bought it because i wanted to do some test and try to build a Security testing device, im developing a GUI based bluetooth scanner, and coding some Python tools. :)

There are available tools like: nmap, ettercap, aircrack-ng, kismet, rdesktop, and many more!


Here are some photos:


Wfuzz, the web bruteforcer is here...

It's been a while since the last tool were released, with deepbit we were working on a tool for Web Application testing, based on bruteforcing, very fast and useful. It can bruteforce GET and POST parameters, unlinked resources (directories, servlets, scripts), etc. It was used during our latest pentest and it shielded very good results. In the package is included a lot of dictionaries tailored for known applications like Weblogic, Websphere, Tomcat, IIS, Apache, Vignette, Fatwire, and many many more (thanks to Darkraver for letting us using Dirb's dictionaries).

Right now the ouput could be the console and a html file. The last one, is very useful for checking the results in the browser, and if you bruteforced a POST parameter, it will create a button in the Html that will send all the POST data, very cool.

If you are a pentester, you must have it ;)

Please check the Wfuzz page.